 NodeCrypto
RSA decryption from N, e and d
Builds an RSA private key from its components N, e and d, then decrypts an RSA-OAEP ciphertext with it. Uses a throw-away test key.
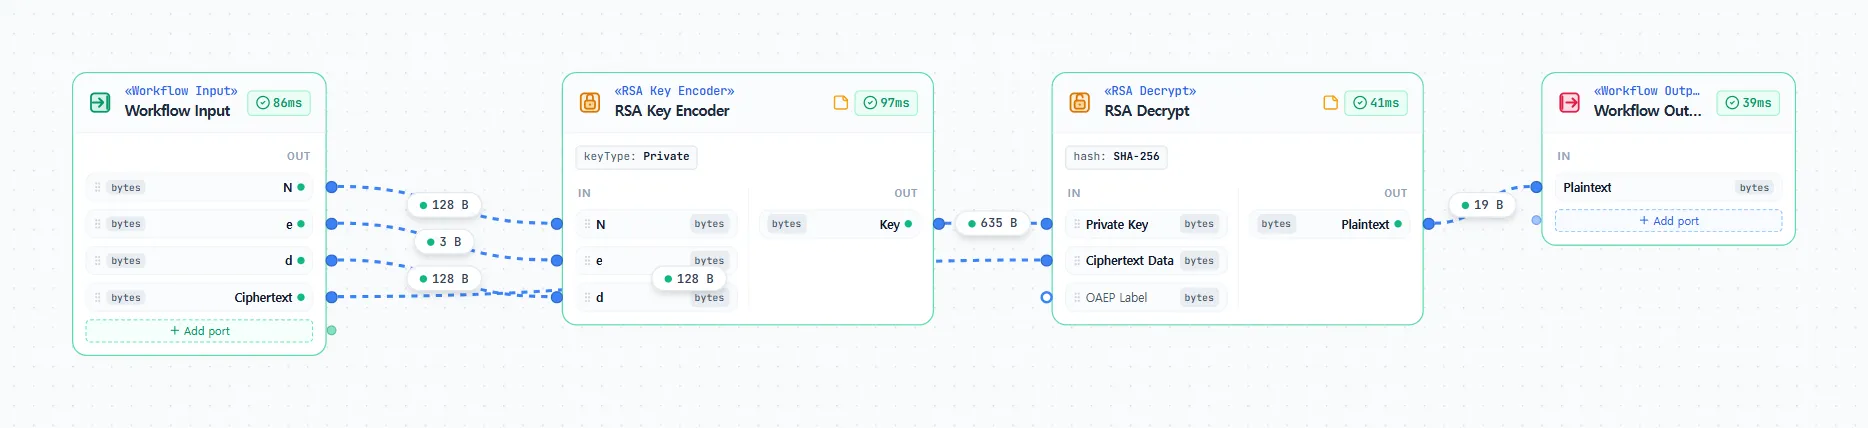
Overview & Cryptographic Context
An RSA key is nothing more than a few large integers. The modulus N = p × q and the public exponent e form the public key; the private exponent d with e · d ≡ 1 (mod λ(N)) completes the private key. Textbooks, standards and test vectors usually print exactly these three numbers, but cryptographic libraries want a key in a standard container such as PKCS#8.
This workflow closes that gap. RSA Key Encoder takes N, e and d, recovers the two prime factors from them (NIST SP 800-56B Rev. 2, Appendix C), checks that they multiply to N and that d inverts e, and writes a PKCS#8 private key. RSA Decrypt then removes the RSA-OAEP padding (RFC 8017, SHA-256, empty label) and returns the message.
The key is a throw-away 1024-bit test key generated for this example and used for nothing else. The ciphertext was produced by Node crypto (OpenSSL), an implementation independent of NodeCrypto, so a matching result confirms the whole chain. 1024 bits is too small for real use; it only keeps the numbers short enough to read.
Pipeline Architecture & Wiring Flow
- Components and ciphertext ingress (
Workflow Input): SuppliesN,e,dand theCiphertextas bytes, in big-endian order without leading zero bytes. - Key assembly (
RSA Key Encoder): WithkeyType = "Private"thedinput appears. The node computes p and q, derives the CRT values and outputs the PKCS#8 private key. - OAEP decryption (
RSA Decrypt): Uses that key withhash = "SHA-256"and returns the original message. - Result (
Workflow Output): Emits the recovered message on thePlaintextport: the 19 ASCII bytes of"RSA from N, e and d".
Nodes & Configuration
| Node | Node Role & Key Parameters | Count |
|---|---|---|
| Workflow Input | Supplies N, e, d and Ciphertext | 1 |
| RSA Key Encoder | Configured with keyType = "Private" | 1 |
| RSA Decrypt | Configured with hash = "SHA-256" | 1 |
| Workflow Output | Collects the Plaintext output | 1 |
Inputs, Outputs & Test Vector Verification
Verification Source: Independent implementation check, Node crypto (OpenSSL RSA-OAEP, SHA-256) on a freshly generated 1024-bit test key (e = 65537) used for nothing else; no published vector
Inputs
| Name | Type | Value (Hex) |
|---|---|---|
N | bytes (128 B, modulus) | ea3a35a2d7b5467e45de0eecd49862cf702dfd6bd59ec103d43543f52b78e92af38951f499bff434a3bd7b50b0a58422fc19ae93d39de392c2b8e21bf4684686d3caaed79121917697335afdd7282928b78e75f36cc5d1dcf16126b1e10d8956d51f270739e3670304961a55757edf4b01e5073df545abaf5dab0acee3046c1f |
e | bytes (3 B, 65537) | 010001 |
d | bytes (128 B, private exponent) | dae08e629fe47bfd5fd8c465b7bcb70955b10452128b899ec45d0a263efb7c1870ffef9ffd550d256ba59368b1c9da12bf365897377721c4714647b50bcdada862f6114300104514fe1cb76c514615082218f68c9726a929547f37fc40fa630032c5eb2c6e95b49ddb98ffdb794b3ba8981654314aee0bf7ee79bb3bc71b4a71 |
Ciphertext | bytes (128 B, RSA-OAEP with SHA-256) | 358db60d0905e619e75119df0bd4603287a65543cb40535d2d44605e2466b36dafd2a5927c72f6dafc1fdcb9f60115340c64b788a5f8203ecb080957bf420b4b40c4e5de4861809cb42b05a1091ea711a650d4239f2faf0684cbeb8c80c9a395f87cc80334310e438e1c465cae5a5fbdc451a20ee68a322e49796198f0088577 |
Expected Outputs
| Name | Type | Value (Hex) |
|---|---|---|
Plaintext | bytes (19 B, ASCII "RSA from N, e and d") | 5253412066726f6d204e2c206520616e642064 |