 NodeCrypto
DID Auth: client
Client side of a challenge-response over ECDH: derives the MAC that answers the server's nonce.
For explaining a protocol only. Do not use this in a real service. The keys shown are public demo keys.
Overview & Cryptographic Context
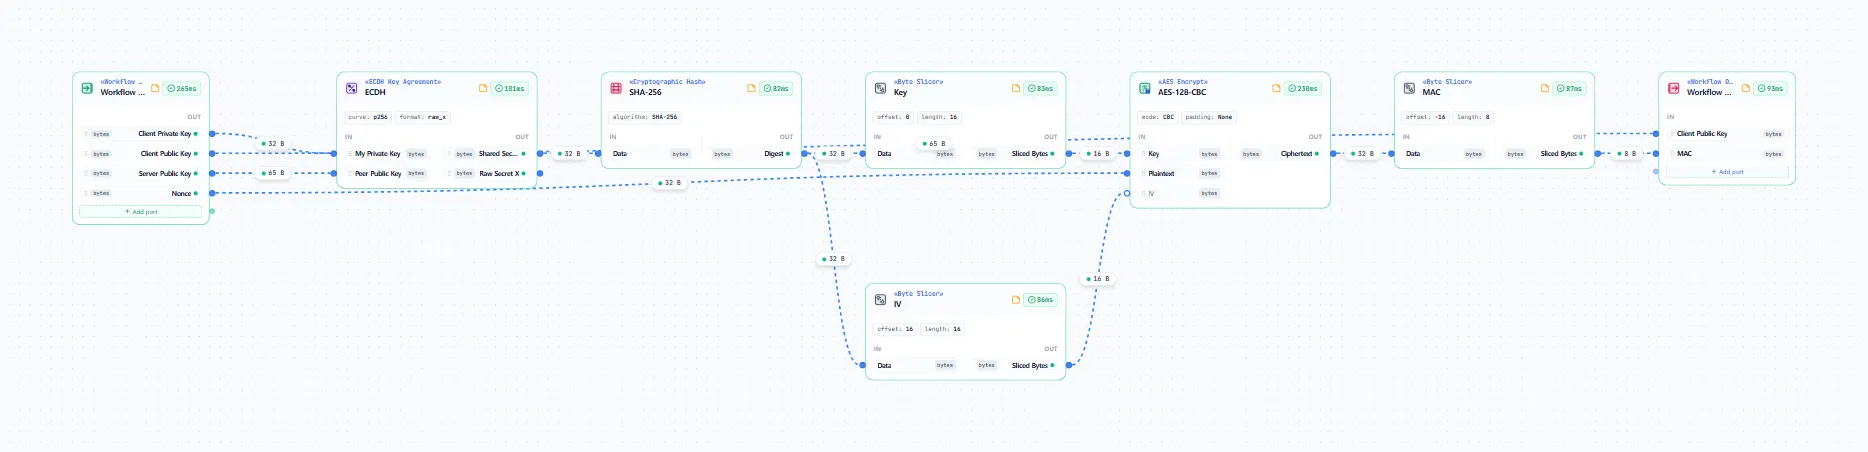
This workflow is Part 2 of the four-part DID Auth learning suite (Key Pairs → Client → Server → End-to-End Demo). It models the client side of an ECDH challenge-response authentication protocol: the server sends its P-256 public key and a 32-byte challenge Nonce, and the client must prove possession of the private key corresponding to its DID document public key without ever transmitting the private key.
The client computes the P-256 ECDH shared secret Z (raw_x, 32 B), hashes D = SHA-256(Z) (32 B), splits D into a 16-byte AES-128 key (D[0..16]) and a 16-byte IV (D[16..32]), encrypts the 32-byte challenge nonce with AES-128-CBC (Padding = None), and extracts the first 8 bytes of the final 16-byte ciphertext block (offset = -16, length = 8) as an 8-byte response MAC.
Pipeline Architecture & Wiring Flow
- Shared Secret Agreement (
ECDH Key Agreement): CombinesClient Private Key(32 B) andServer Public Key(65 B) on curvep256to output the 32-byte X coordinate. - Key & IV Partitioning (
Cryptographic Hash+Byte Slicer× 2): Hashes the shared secret withSHA-256and slices bytes0..16asKeyand bytes16..32asIV. - Challenge Encryption & Truncation (
AES Encrypt+Byte Slicer): Encrypts the 32-byteNonceinCBCmode (Padding = None) and slices 8 bytes from the start of the last ciphertext block (offset = -16, length = 8) to emitMACalongsideClient Public Key.
Nodes & Configuration
| Node | Node Role & Key Parameters | Count |
|---|---|---|
| Workflow Input | Supplies Client Private Key, Client Public Key, Server Public Key, and Nonce | 1 |
| ECDH Key Agreement | curve = "p256", format = "raw_x" (32-byte shared secret) | 1 |
| Cryptographic Hash | algorithm = "SHA-256" | 1 |
| Byte Slicer | Three instances: Key (0, 16), IV (16, 16), and MAC (-16, 8) | 3 |
| AES Encrypt | Labeled AES-128-CBC; configured with mode = "CBC", padding = "None" | 1 |
| Workflow Output | Emits Client Public Key (65 B) and MAC (8 B) | 1 |
Inputs, Outputs & Test Vector Verification
Verification Source: independent implementation: Node crypto (reference/did-auth/did-auth.mjs), no published vector
Inputs
| Name | Type | Value (Hex) |
|---|---|---|
Client Private Key | bytes (32 B) | 2ad39d172118c0802359e6806b8939881b6a3fbcc9e89e307499a862acd4e3c9 |
Client Public Key | bytes (65 B) | 0415dc193b8e2a688d603303e85ec8fcc15dcba44ef2156a128c386b66b4f5e1d2188e7ca9d0385c02e72c6899f2771e86bb017a2d2903d89a2892c2199aec8f4d |
Server Public Key | bytes (65 B) | 0447edf45c2c402ae4cfe8460fb208fbc0d6af18efa4b3d78d44c73fcb0c250ec08222f152af03468af65a74fbf89ecc763f19b0dadec5fd8df5cf76d7da097ae5 |
Nonce | bytes (32 B) | 000102030405060708090a0b0c0d0e0f101112131415161718191a1b1c1d1e1f |
Expected Outputs
| Name | Type | Value (Hex) |
|---|---|---|
Client Public Key | bytes (65 B) | 0415dc193b8e2a688d603303e85ec8fcc15dcba44ef2156a128c386b66b4f5e1d2188e7ca9d0385c02e72c6899f2771e86bb017a2d2903d89a2892c2199aec8f4d |
MAC | bytes (8 B) | 39b415c1dfeb8f52 |