 NodeCrypto
DID Auth: server
Server side: recomputes the MAC from its own private key and compares it with the MAC sent by the client.
For explaining a protocol only. Do not use this in a real service. The keys shown are public demo keys.
Overview & Cryptographic Context
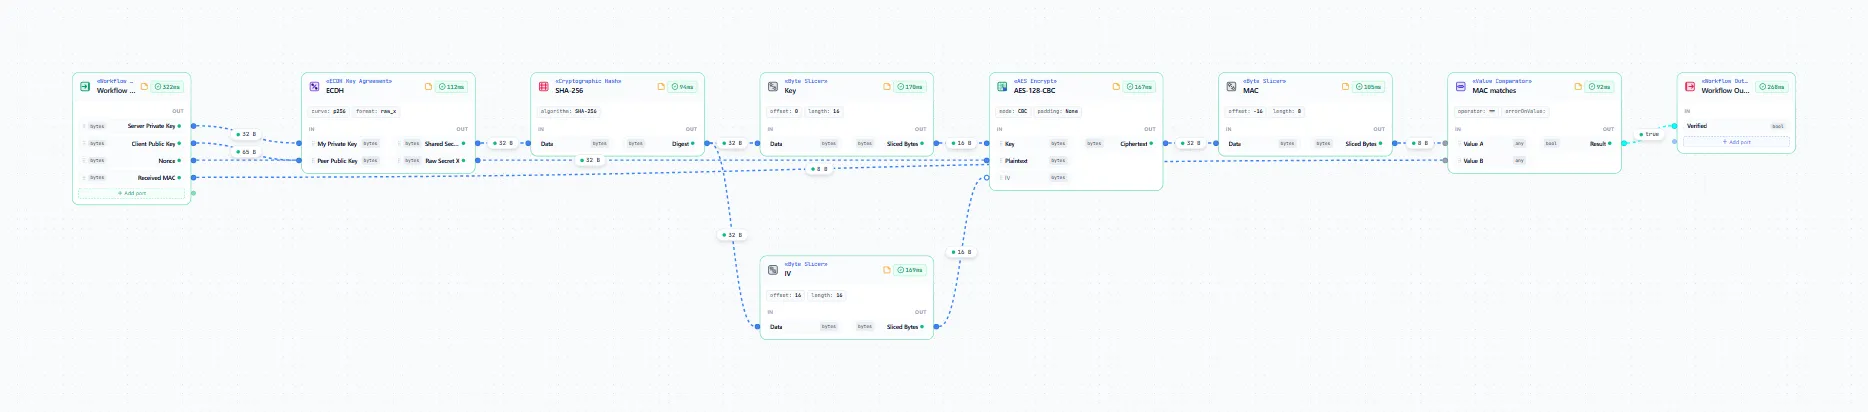
This workflow is Part 3 of the four-part DID Auth learning suite (Key Pairs → Client → Server → End-to-End Demo). Upon receiving the client's 65-byte P-256 public key and 8-byte response Received MAC, the server performs ECDH using its own 32-byte Server Private Key and the Client Public Key.
By the commutativity of scalar multiplication on elliptic curves ([dserver]Qclient = [dserver · dclient]G = [dclient]Qserver), the server derives the exact same 32-byte shared secret, splits SHA-256(Z) into the same 16-byte AES key and 16-byte IV, encrypts its 32-byte challenge Nonce, slices the expected 8-byte MAC, and compares it against Received MAC using a Value Comparator.
Pipeline Architecture & Wiring Flow
- Shared Secret Reconstruction (
ECDH Key Agreement): Computes the 32-byte P-256 shared secret fromServer Private KeyandClient Public Key. - Expected MAC Recomputation (
SHA-256→Byte Slicer× 2 →AES-128-CBC→Byte Slicer): Reconstructs the 8-byte MAC39b415c1dfeb8f52over the 32-byte challengeNonce. - Constant-Time Verdict (
Value Comparator): Compares the recomputed 8-byte slice (a) withReceived MAC(b) using operator==and outputsVerified = true.
Nodes & Configuration
| Node | Node Role & Key Parameters | Count |
|---|---|---|
| Workflow Input | Supplies Server Private Key, Client Public Key, Nonce, and Received MAC | 1 |
| ECDH Key Agreement | curve = "p256", format = "raw_x" | 1 |
| Cryptographic Hash | algorithm = "SHA-256" | 1 |
| Byte Slicer | Three instances: Key (0, 16), IV (16, 16), and MAC (-16, 8) | 3 |
| AES Encrypt | Labeled AES-128-CBC; configured with mode = "CBC", padding = "None" | 1 |
| Value Comparator | Labeled MAC matches; configured with operator = "==" | 1 |
| Workflow Output | Emits boolean verdict Verified | 1 |
Inputs, Outputs & Test Vector Verification
Verification Source: independent implementation: Node crypto (reference/did-auth/did-auth.mjs), no published vector
Inputs
| Name | Type | Value (Hex) |
|---|---|---|
Server Private Key | bytes (32 B) | a4b87f7821ada85b4e7f63618924b4c3f3bbb78cddcab485a7ee6f15fdfc7261 |
Client Public Key | bytes (65 B) | 0415dc193b8e2a688d603303e85ec8fcc15dcba44ef2156a128c386b66b4f5e1d2188e7ca9d0385c02e72c6899f2771e86bb017a2d2903d89a2892c2199aec8f4d |
Nonce | bytes (32 B) | 000102030405060708090a0b0c0d0e0f101112131415161718191a1b1c1d1e1f |
Received MAC | bytes (8 B) | 39b415c1dfeb8f52 |
Expected Outputs
| Name | Type | Value |
|---|---|---|
Verified | bool | true |