 NodeCrypto
DID Auth: key pairs
Generates the P-256 key pairs of the DID Auth demo, one for the server and one for the client. Public demo keys only.
For explaining a protocol only. Do not use this in a real service. The keys shown are public demo keys.
Overview & Cryptographic Context
This workflow is Part 1 of the four-part DID Auth challenge-response protocol walkthrough (Key Pairs → Client → Server → End-to-End Demo). In decentralized identifier (DID) authentication over elliptic curves, both the relying party (Server) and the holder (Client) possess long-term or ephemeral key pairs on NIST P-256 (secp256r1).
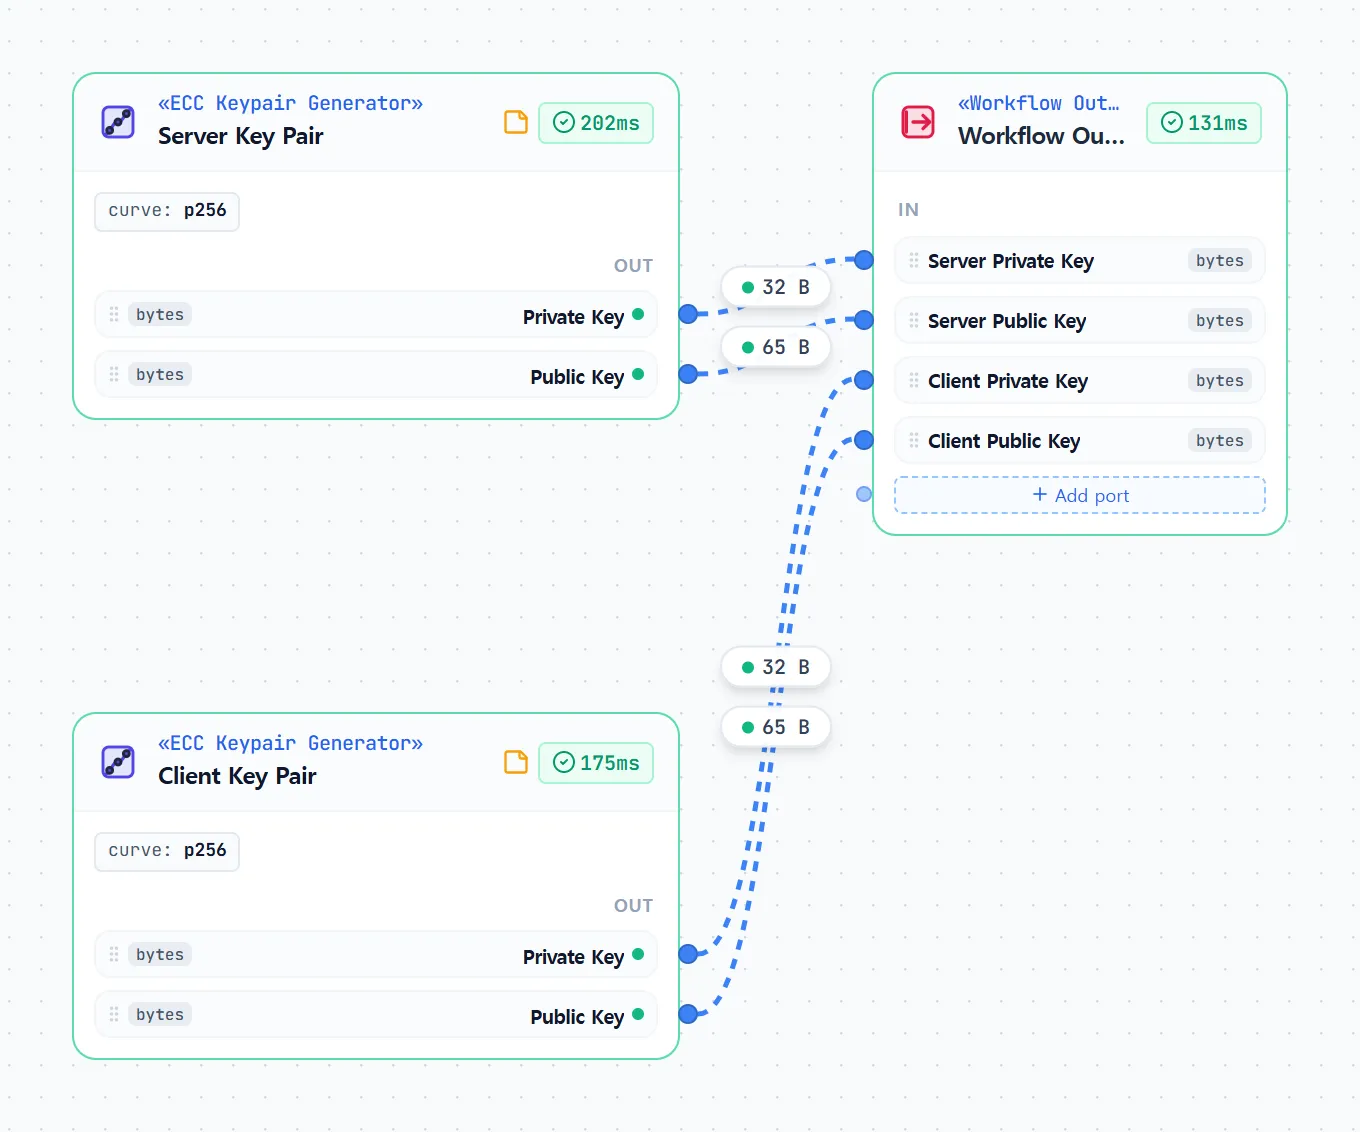
Running this graph generates two independent P-256 key pairs using the browser's CSPRNG: each party receives a 32-byte private scalar and a 65-byte uncompressed SEC 1 public key (0x04 || X || Y).
Pipeline Architecture & Wiring Flow
- Server Key Generation (
Server Key Pair): Configured withcurve = "p256". EmitsServer Private Key(32 B) andServer Public Key(65 B). - Client Key Generation (
Client Key Pair): Configured withcurve = "p256". EmitsClient Private Key(32 B) andClient Public Key(65 B). - Output Collection (
Workflow Output): Exposes all four keys on named output ports so they can be inspected or copied into the DID Auth: client and DID Auth: server workflows.
Nodes & Configuration
| Node | Node Role & Key Parameters | Count |
|---|---|---|
| ECC Keypair Generator | Two instances (Server Key Pair, Client Key Pair) configured with curve = "p256" | 2 |
| Workflow Output | Collects the 4 generated private and public keys | 1 |
Outputs & Verification
Verification Source: random key pairs: nothing deterministic to compare; the keys are checked by the did-auth-client and did-auth-server examples
Outputs
| Name | Type | Format & Length |
|---|---|---|
Server Private Key | bytes | 32-byte P-256 secret scalar (random per run) |
Server Public Key | bytes | 65-byte uncompressed SEC 1 point 0x04 || X || Y |
Client Private Key | bytes | 32-byte P-256 secret scalar (random per run) |
Client Public Key | bytes | 65-byte uncompressed SEC 1 point 0x04 || X || Y |